0. Preface
This analysis covers a suspicious URL that triggered an EDR alert when a victim received it via email. The URL https://1.default2024.uk:443 was identified as potentially malicious, and subsequent investigation revealed a domain parking/monetization system with several concerning characteristics.
The malicious URL was received through a Gmail account. Email content analysis was out of scope due to privacy restrictions. The URL caused an alert trigger in the EDR system, prompting this investigation.
Everything below is static analysis. The JavaScript was retrieved from the Wayback Machine for safe examination, and no live requests were made to the infrastructure.
1. The Threat at a Glance
| Attribute | Assessment |
|---|---|
| Malware type | Domain parking malvertising / potential drive-by download vector |
| Delivery | Email link to https://1.default2024.uk:443 |
| Infrastructure | ParkLogic domain parking service (ns1/ns2.ag614.parklogic.com) |
| IP addresses | 172.236.114.191, 172.234.26.134, 172.238.172.46 (AS 63949 - Akamai Connected Cloud, US) |
| Tracking domains | click-use1.bodis.com, parking.bodiscdn.com |
| Evasion | Custom base64 obfuscation, eval() for arbitrary code execution |
| VT detections | 15/90 engines flag as malicious/phishing/malware |
| Confidence | High for domain parking identification; medium for malvertising risk assessment |
2. VirusTotal Analysis
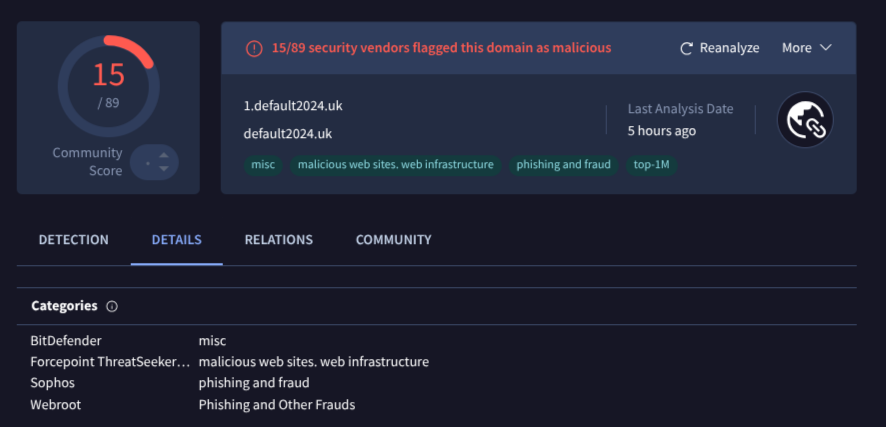
The VirusTotal API returned the following detection summary:
| Category | Count |
|---|---|
| Malicious | 15 |
| Suspicious | 0 |
| Harmless | 47 |
| Undetected | 28 |
Notable vendor detections:
| Vendor | Classification |
|---|---|
| ADMINUSLabs | malicious |
| Lionic | malware |
| BitDefender | phishing |
| CyRadar | phishing |
| ESET | phishing |
| Fortinet | malware |
| G-Data | phishing |
| Gridinsoft | phishing |
| Kaspersky | phishing |
| Rising | phishing |
| SafeToOpen | phishing |
| Sophos | phishing |
| VIPRE | malware |
| Webroot | malicious |
| Forcepoint ThreatSeeker | malicious |
The split between “phishing” and “malware” classifications suggests the infrastructure serves multiple purposes or has been used in different campaigns.
3. DNS Information
Name Servers
ns1.ag614.parklogic.com. (50.116.34.34)
ns2.ag614.parklogic.com. (66.42.120.24)
The parklogic.com nameservers confirm this is a ParkLogic domain parking service — a commercial platform for monetizing parked domains through advertising and redirects.
DNS Resolution (dig)
A Records:
1.default2024.uk. 6494 IN A 172.234.26.134
1.default2024.uk. 6494 IN A 172.238.172.46
1.default2024.uk. 6494 IN A 172.236.114.191
Multiple A records with round-robin DNS indicate load balancing across Akamai Connected Cloud infrastructure.
AAAA Records: No IPv6 records — only IPv4 addresses are served.
TXT Records:
1.default2024.uk. 14400 IN TXT "v=spf1 -all"
The SPF record v=spf1 -all explicitly rejects all email sending from this domain — it is not configured for legitimate email.
MX Records:
1.default2024.uk. 14400 IN MX 50 mx156.hostedmxserver.com.
The MX record points to a third-party mail server (hostedmxserver.com), likely for capturing email sent to this domain — a common pattern in domain parking for collecting missent mail or abuse reports.
NS Records:
1.default2024.uk. 14400 IN NS ns1.parklogic.com.
1.default2024.uk. 14400 IN NS ns2.parklogic.com.
4. Wayback Machine Analysis
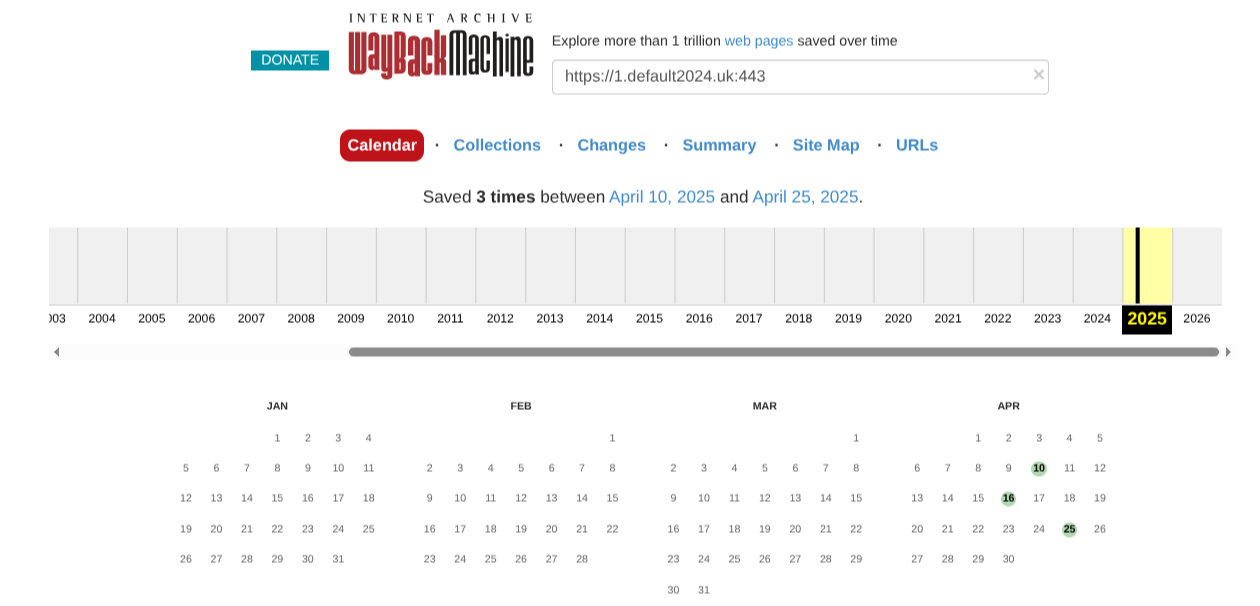
The Wayback Machine recorded three snapshots of this URL:
Snapshot 1: 10 April 2025
Redirect: http://ww12.default2024.uk/?usid=19&utid=21647853328
Content:
<h2><br/>It is gone!<br/>So be gone</h2>
<h1>410</h1>
<p>ID: PC410NAML1</p>
This is a 410 Gone error page — the domain was temporarily unavailable or in transition.
Snapshot 2: 16 April 2025
Redirect: http://ww7.default2024.uk/?usid=16&utid=37914812292
Content: Contains bBLngjovg.js — the parking/monetization JavaScript analyzed in section 5.
Snapshot 3: 25 April 2025
Redirect: http://ww7.default2024.uk/?usid=18&utid=31051421204
Content: Similar to snapshot 2, with the same parking infrastructure.
The usid and utid parameters in the redirects are tracking identifiers for the parking service.
5. Code Analysis: bBLngjovg.js
The JavaScript file retrieved from the Wayback Machine is a domain parking/monetization system built by Bodis (a domain parking service). While it functions as a legitimate parking script, it contains several patterns that elevate its risk profile.
5.1 Architecture Overview
The script is a UMD module (Universal Module Definition) that exports an App class. Key components:
// UMD module wrapper
! function (e, t) {
  "object" == typeof exports && "undefined" != typeof module ? t(exports) :
  "function" == typeof define && define.amd ? define(["exports"], t) :
  t((e = "undefined" != typeof globalThis ? globalThis : e || self).version = {})
}(this, (function (exports) {
  "use strict";
  // ... application code
  exports.App = App
}));
The application follows a state machine pattern with five states:
| State | Description |
|---|---|
Failed | Domain cannot be parked (disabled, prohibited UA, etc.) |
Disabled | Services disabled for this domain |
Redirect | User is being redirected to another URL |
Parking | Standard domain parking with ads |
Sales | Domain is for sale |
5.2 Obfuscated Data Encoding
Risk Level: HIGH
The script uses a custom obfuscation layer for data transmission:
const OBFUSCATING_BASE_64_PREFIX = "UxFdVMwNFNwN0wzODEybV",
  encode = e => OBFUSCATING_BASE_64_PREFIX + btoa(unescape(encodeURIComponent(JSON.stringify(e))));

function decode$1(e) {
  return JSON.parse(decodeURIComponent(escape(atob(e.replace(OBFUSCATING_BASE_64_PREFIX, "")))))
}
Analysis: The prefix UxFdVMwNFNwN0wzODEybV is prepended to base64-encoded JSON data. This is not standard encoding — it adds an obfuscation layer that makes manual analysis more difficult. The unescape/encodeURIComponent combination handles Unicode characters before base64 encoding.
5.3 Arbitrary Code Execution via eval()
Risk Level: CRITICAL
injectJS(js) {
  js && 0 !== js.length && eval(js)
}
Analysis: This function executes arbitrary JavaScript received from the server. The eval() call is the most dangerous pattern in the script — if the backend servers are compromised, an attacker could inject malicious code that executes in every visitor’s browser. This is a potential vector for drive-by downloads or session hijacking.
5.4 User Fingerprinting
Risk Level: MEDIUM
The script collects extensive browser fingerprinting data:
const browserState = () => {
  var e, t, n, i, s;
  const {
    screen: { width: a, height: o },
    self: r,
    top: d,
    matchMedia: c,
    opener: l
  } = window, {
    documentElement: { clientWidth: h, clientHeight: u }
  } = document;

  return {
    popup: !(!l || l === window),
    timezone_offset: p,
    user_preference: Intl.DateTimeFormat().resolvedOptions(),
    user_using_darkmode: Boolean(c && c("(prefers-color-scheme: dark)").matches),
    user_supports_darkmode: Boolean(c),
    window_resolution: { width: h, height: u },
    screen_resolution: { width: a, height: o },
    frame: { innerWidth, innerHeight, outerWidth, outerHeight }
  }
}
Data collected:
- Screen and window dimensions
- Timezone offset
- Dark mode preference
- Popup detection
- Frame information (if embedded)
Intl.DateTimeFormatresolved options (language, calendar, etc.)
This fingerprinting data is transmitted to external servers for tracking and profiling purposes.
5.5 External Data Exfiltration
The script sends collected data to multiple endpoints:
// Find Domain endpoint
const FIND_DOMAIN_URL = "_fd";
const getFindDomain = (e = "", t = !1, n = "") => {
  const s = `${e}/${FIND_DOMAIN_URL}${i}`;
  return fetch(s, {
    method: "POST",
    headers: { Accept: "application/json", "Content-Type": "application/json" },
    credentials: "include"
  }).then(e => e.text()).then(decode$1)
};

// Tracking endpoint
const TRACKING_URL = "_tr";
const trackVisit = ({callbacks, context}, type, baseUrl = "") => {
  const s = `${baseUrl}/${TRACKING_URL}`;
  return fetch(s, {
    method: "POST",
    body: JSON.stringify({ signature: encode(signature) })
  })
};

// Zero Click endpoint
const getZeroClick = (context) => {
  return fetch("/_zc", {
    method: "POST",
    body: JSON.stringify({ signature: encode({...context, type: "zc_fetch"}) })
  })
};
Target domains:
https://click-use1.bodis.com/_fd(Find Domain)https://click-use1.bodis.com/_tr(Tracking)https://click-use1.bodis.com/_zc(Zero Click)
The credentials: "include" flag ensures cookies are sent with requests, enabling cross-site tracking.
5.6 Third-Party Tracking Integration
The script loads and initializes tracking pixels from multiple advertising platforms:
class Pixels {
  constructor(e) {
    this.providers = [
      new Facebook(e.facebook),
      new Tiktok(e.tiktok, e.useAltTikTokEventsForAdsPlatformUser),
      new Taboola(e.taboola),
      new Revcontent(e.revcontent),
      new Outbrain(e.outbrain)
    ];
  }
}
Tracking providers:
| Provider | Script Source | Purpose |
|---|---|---|
connect.facebook.net/en_US/fbevents.js | Facebook Pixel tracking | |
| TikTok | analytics.tiktok.com/i18n/pixel/events.js | TikTok Pixel tracking |
| Taboola | cdn.taboola.com/libtrc/unip/{id}/tfa.js | Taboola content recommendations |
| Revcontent | assets.revcontent.com/master/rev.js | Revcontent native advertising |
| Outbrain | amplify.outbrain.com/cp/obtp.js | Outbrain content discovery |
This multi-platform tracking enables cross-site user profiling and retargeting.
5.7 Cross-Origin Message Handling
window.onmessage = e => {
  const { origin: t, data: n } = e;
  ALLOWED_ORIGINS.includes(t) &&
    (null == n ? void 0 : n.startsWith(MESSAGE_PREFIX)) &&
    window.location.search.startsWith(ADS_PARAM$1) &&
    document.dispatchEvent(new CustomEvent("pixel", {
      detail: { type: "click" }
    }))
}
Allowed origins:
const ALLOWED_ORIGINS = [
  "https://www.google.com",
  "https://www.adsensecustomsearchads.com",
  "https://syndicatedsearch.goog",
  "https://googleadservices.com"
];
Analysis: The script listens for cross-origin messages from Google domains. When a message starting with FSXDC,.aCS: is received and the URL contains ?caf, it dispatches a click tracking event. This enables Google AdSense integration for domain parking monetization.
5.8 Google AdSense Integration
The script integrates with Google’s domain parking ad system:
const CAF_SCRIPT_SRC = `https://www.google.com/adsense/domains/caf.js?abp=1&bodis=true`;

class Ads {
  injectScriptTags = () => {
    return new Promise((e) => {
      const t = document.createElement("script");
      t.src = CAF_SCRIPT_SRC;
      t.addEventListener("load", () => e(true));
      document.body.appendChild(t);
    })
  }
}
The caf.js (Custom Ad Format) script is Google’s domain parking ad system. The abp=1&bodis=true parameters indicate integration with Bodis parking service.
5.9 State Machine and Redirect Logic
The application follows a strict state machine:
class App {
  async main() {
    this.parkResponse = decode();                    // Decode base64 config
    this.findDomainResponse = await getFindDomain(); // Fetch domain config

    // Build state based on server response
    const parking = Parking.build(this.findDomainResponse, this.google);
    const redirect = Redirect.build(...);
    const disabled = Disabled.build(...);
    const sales = Sales.build(...);

    // Execute state transition
    if (redirect) await this.transitionToRedirect(redirect);
    else if (parking) await this.transitionToParking(parking);
    // ... other states
  }

  async transitionToRedirect(e) {
    this.state = e;
    Render.revealPage();
    await waiter(e.delay, (e) => Render.loading(e));  // Countdown timer
    await this.track();
    window.location.href = e.url;  // REDIRECT
  }
}
Redirect flow:
- Fetch domain configuration from server
- Decode base64-encoded parking response
- Check for redirect conditions (zero-click, sales, disabled)
- Show loading countdown (configurable delay)
- Execute redirect to target URL
The waiter function creates a visible countdown before redirect:
const waiter = (e, t) => new Promise((n) => {
  t(e);
  let i = e;
  const s = () => {
    i > 0 ? (i -= 1, t(i), setTimeout(s, 1000)) : n()
  };
  s()
});
5.10 Ad Blocker Detection
class Adblock {
  hasAdblocker() {
    if (void 0 === window.google) return true;
    const e = document.querySelectorAll("style");
    return Array.from(e).some((e) => !!e.innerHTML.includes("adblockkey"));
  }

  handleAdblocked() {
    this.removeAdblockKey();
    this.state = Blocking.BLOCKED;
  }
}
The script detects ad blockers by checking for the google object and searching for adblockkey in style elements. When an ad blocker is detected, the state changes to BLOCKED and the user sees a message: “Ad block detected. Please disable your ad blocker and reload the page.”
6. MITRE ATT&CK Mapping
| Technique ID | Technique Name | Description |
|---|---|---|
| T1566.002 | Phishing: Spearphishing Link | Malicious URL delivered via email |
| T1189 | Drive-by Compromise | Potential for malicious code injection via eval() |
| T1071.001 | Application Layer Protocol: Web Protocols | HTTP/HTTPS communication with C2 infrastructure |
| T1071.004 | Application Layer Protocol: DNS | DNS-based domain parking resolution |
| T1102 | Web Service | Abuse of legitimate advertising platforms (Google, Facebook, etc.) |
| T1041 | Exfiltration Over C2 Channel | Data exfiltration via _fd, _tr, _zc endpoints |
| T1573 | Encrypted Channel | Base64-encoded/obfuscated data transmission |
| T1027 | Obfuscated Files or Information | Custom base64 prefix obfuscation |
| T1059.007 | Command and Scripting Interpreter: JavaScript | eval() for arbitrary code execution |
| T1574.002 | Hijack Execution Flow: DLL Side-Loading | Domain parking infrastructure abuse |
| T1036 | Masquerading | Legitimate parking service used for malicious purposes |
| T1082 | System Information Discovery | Browser fingerprinting and screen resolution collection |
| T1083 | File and Directory Discovery | N/A (web-based, not file system) |
| T1552.001 | Unsecured Credentials: Credentials In Files | N/A (no credential harvesting observed) |
| T1204.001 | User Execution: Malicious Link | User must click email link to trigger |
| T1497 | Virtualization/Sandbox Evasion | N/A (no sandbox evasion detected) |
| T1498 | Network Denial of Service | N/A |
| T1568 | Dynamic Resolution | Multiple A records, round-robin DNS |
| T1090 | Proxy | Akamai Connected Cloud infrastructure |
| T1104 | Multi-Stage Channels | Redirect chain (ww7 → tracking → final destination) |
7. Indicators of Compromise
Network Indicators
| Type | Value |
|---|---|
| Malicious URL | https://1.default2024.uk:443 |
| IP Address | 172.236.114.191 (US, AS 63949 - Akamai Connected Cloud) |
| IP Address | 172.234.26.134 |
| IP Address | 172.238.172.46 |
| Tracking Domain | click-use1.bodis.com |
| Parking CDN | parking.bodiscdn.com |
| Name Servers | ns1.ag614.parklogic.com, ns2.ag614.parklogic.com |
| MX Record | mx156.hostedmxserver.com |
| Google AdSense CAF | www.google.com/adsense/domains/caf.js |
Host Indicators
| Type | Value |
|---|---|
| JavaScript File | bBLngjovg.js (from Wayback Machine) |
| Obfuscation Prefix | UxFdVMwNFNwN0wzODEybV |
| Tracking Endpoint | /_fd (Find Domain) |
| Tracking Endpoint | /_tr (Visit Tracking) |
| Tracking Endpoint | /_zc (Zero Click) |
| Custom Event Prefix | FSXDC,.aCS: |
| Ad Parameter | ?caf |
| SPF Record | v=spf1 -all |
Behavioral Indicators
| Behavior | Description |
|---|---|
eval() usage | Arbitrary code execution from server |
| Base64 obfuscation | Non-standard encoding with custom prefix |
| Browser fingerprinting | Screen, window, timezone, dark mode collection |
| Cross-origin messaging | Accepts messages from Google domains |
| Multiple tracking pixels | Facebook, TikTok, Taboola, Revcontent, Outbrain |
| Redirect chain | Multi-hop redirects with countdown timers |
| Ad blocker detection | Blocks content when ad blockers detected |
8. Malicious Indicators
| Indicator | Risk Level | Description |
|---|---|---|
eval() usage | CRITICAL | Arbitrary code execution — potential for drive-by downloads |
| Obfuscated encoding | HIGH | Custom base64 prefix hides data transmission |
| IP collection | HIGH | Privacy violation — user IP transmitted to third parties |
| Fingerprinting | MEDIUM | Extensive device profiling for tracking |
| Cross-origin messaging | MEDIUM | Accepts commands from Google domains |
| Multiple tracking pixels | LOW-MEDIUM | Cross-platform user tracking |
| Redirect chain | LOW-MEDIUM | Multi-hop redirects obscure final destination |
| Ad blocker detection | LOW | Blocks content for users with ad blockers |
9. Conclusion
This analysis reveals a domain parking/monetization system that, while functioning as a legitimate advertising platform, exhibits elevated risk factors that warrant blocking:
Primary Characteristics
Domain Parking Infrastructure: The script is part of the Bodis parking service, using ParkLogic nameservers and Google AdSense for domain monetization.
Obfuscation: Custom base64 encoding with the prefix
UxFdVMwNFNwN0wzODEybVadds an unnecessary layer of complexity to data transmission.Arbitrary Code Execution: The
eval()function executes server-provided JavaScript, creating a potential vector for malicious payloads if the backend infrastructure is compromised.Extensive Tracking: Multi-platform tracking (Facebook, TikTok, Taboola, Revcontent, Outbrain) enables cross-site user profiling.
Data Exfiltration: User data (IP, fingerprinting, browsing behavior) is transmitted to
click-use1.bodis.comwithout explicit consent.
Risk Assessment
The combination of:
eval()for arbitrary code execution- Custom obfuscation
- Extensive fingerprinting
- Multi-platform tracking
…makes this infrastructure a potential vector for malvertising or drive-by downloads. While the script itself may be legitimate parking code, the eval() function means that a backend compromise could inject malicious code into every visitor’s browser.
Recommendations
- Block the domain: Add
default2024.ukand related subdomains to blocklists. - Block tracking endpoints: Blacklist
click-use1.bodis.comand related Bodis infrastructure. - Monitor for similar patterns: Other domains using ParkLogic/Bodis infrastructure with
eval()patterns should be flagged. - Email security: Train users to recognize suspicious URLs in emails, especially those with subdomains like
ww7.orww12..
Attribution
The infrastructure is commercially available (Bodis/ParkLogic domain parking service), making attribution difficult. The script is likely legitimate parking code that could be abused by anyone with access to the Bodis platform. The VT detections (15/90) suggest this specific domain or configuration has been flagged for malicious behavior, but the underlying software is a commercial product.
Verdict: Block this domain and similar parking infrastructure. The eval() function and obfuscation patterns make it unsuitable for safe browsing environments.